Internet Intelligence for Enterprise Exposure Management
Use FullHunt directly for continuous discovery, validated vulnerabilities, dark web monitoring, and change alerts across your external perimeter.
Map your entire external perimeter. Keep it current.
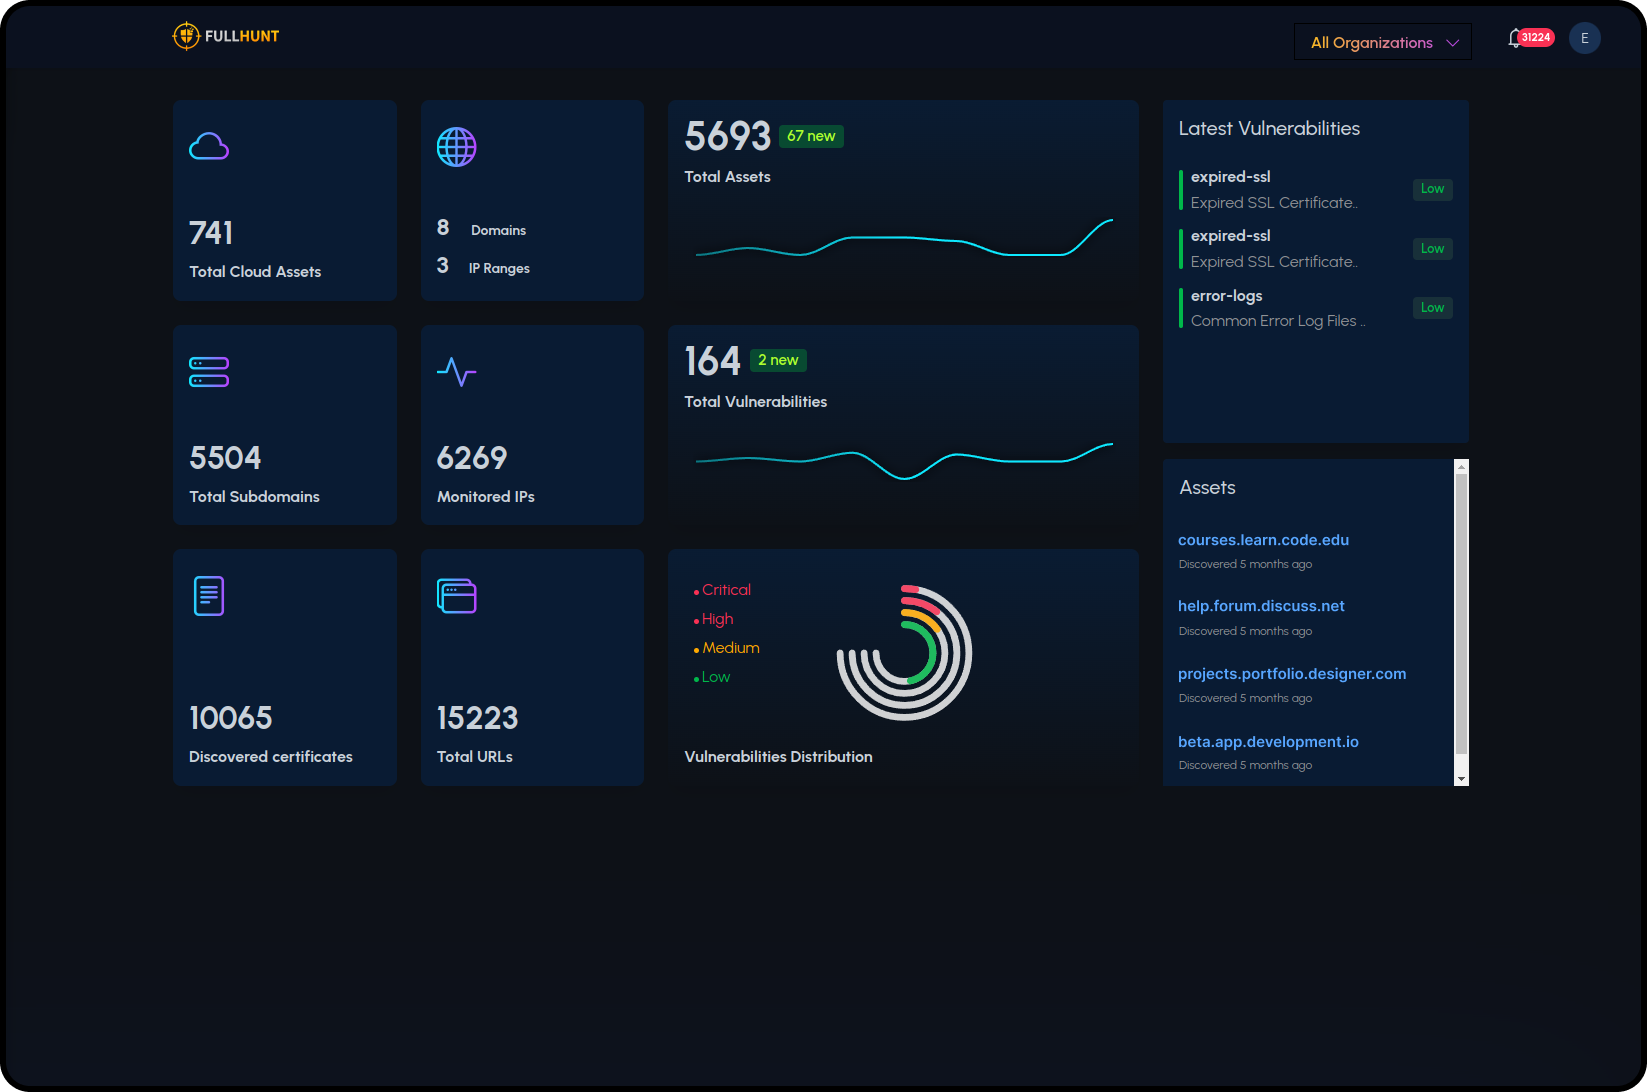
FullHunt discovers domains, subdomains, IPs, cloud services, and tech stacks at internet scale, then monitors them continuously. Shadow IT and forgotten assets surface automatically. FullHunt performs discovery from the public internet and monitors new assets as they appear.
01
Asset Discovery
Internet-scale enumeration of subdomains, IPs, cloud services, and technologies. Continuously updated.
02
Change Monitoring
New services, configuration drift, and exposure changes detected on the collection pass that observes them, with alerts routed where you work.
03
Technology Fingerprinting
7,000+ web and product signatures. Know what's running across your entire perimeter.
04
Cloud Asset Discovery
AWS, Azure, GCP, Alibaba Cloud, Oracle Cloud. Multi-cloud visibility without credentials.
05
Organization Attribution
Assets automatically attributed to business units, subsidiaries, and third-party vendors.
06
Certificate Tracking
TLS certificate monitoring: expiration alerts, mismatches, and shadow certificates surfaced.
Know when your attack surface changes.
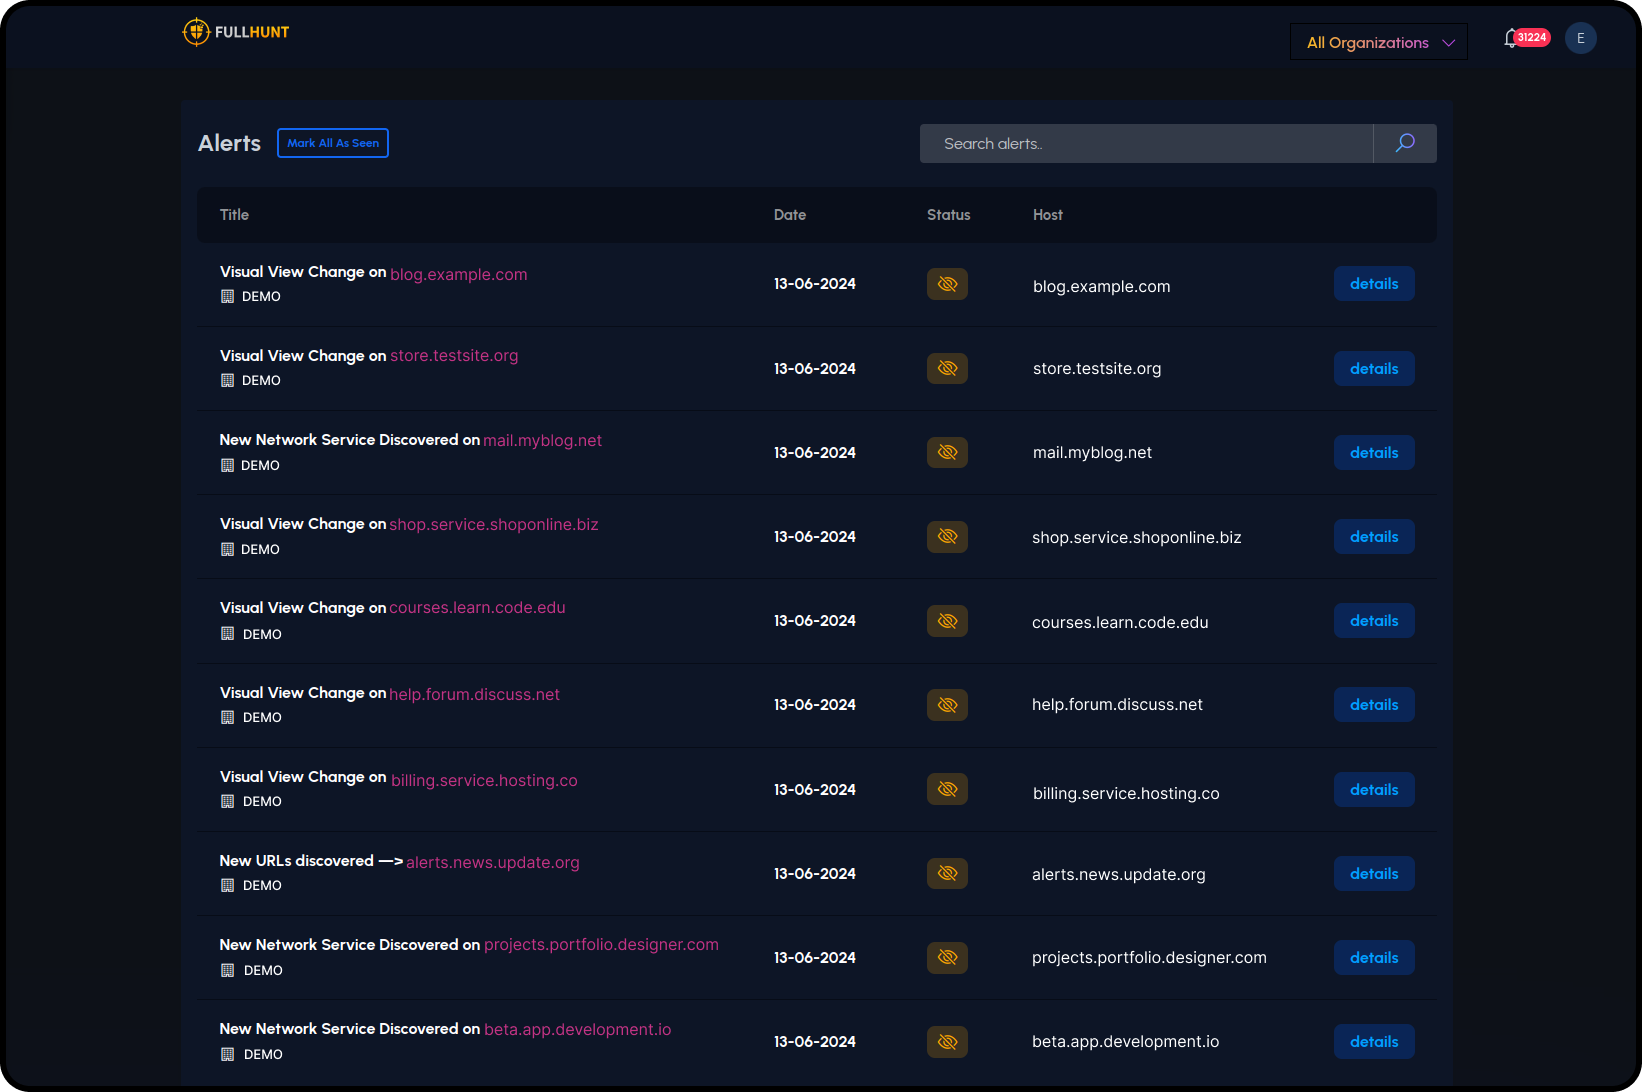
Alerting on visual changes, new services, new URLs, and configuration drift. Every change is logged and attributed.
- Visual change detection
- New network services
- New URLs & endpoints
- Configuration drift alerts
Runtime-validated checks. Not guesswork.
4,000+ vulnerability checks run against live assets. Every finding is confirmed at runtime. False positives get cut before they reach your team.
- 4,000+ vulnerability checks
- Runtime validation for each finding
- EPSS & KEV enrichment built-in
- Public exploit correlation
- Asset scoring by exploitability
Findings confirmed against the live service, ranked by real-world risk.
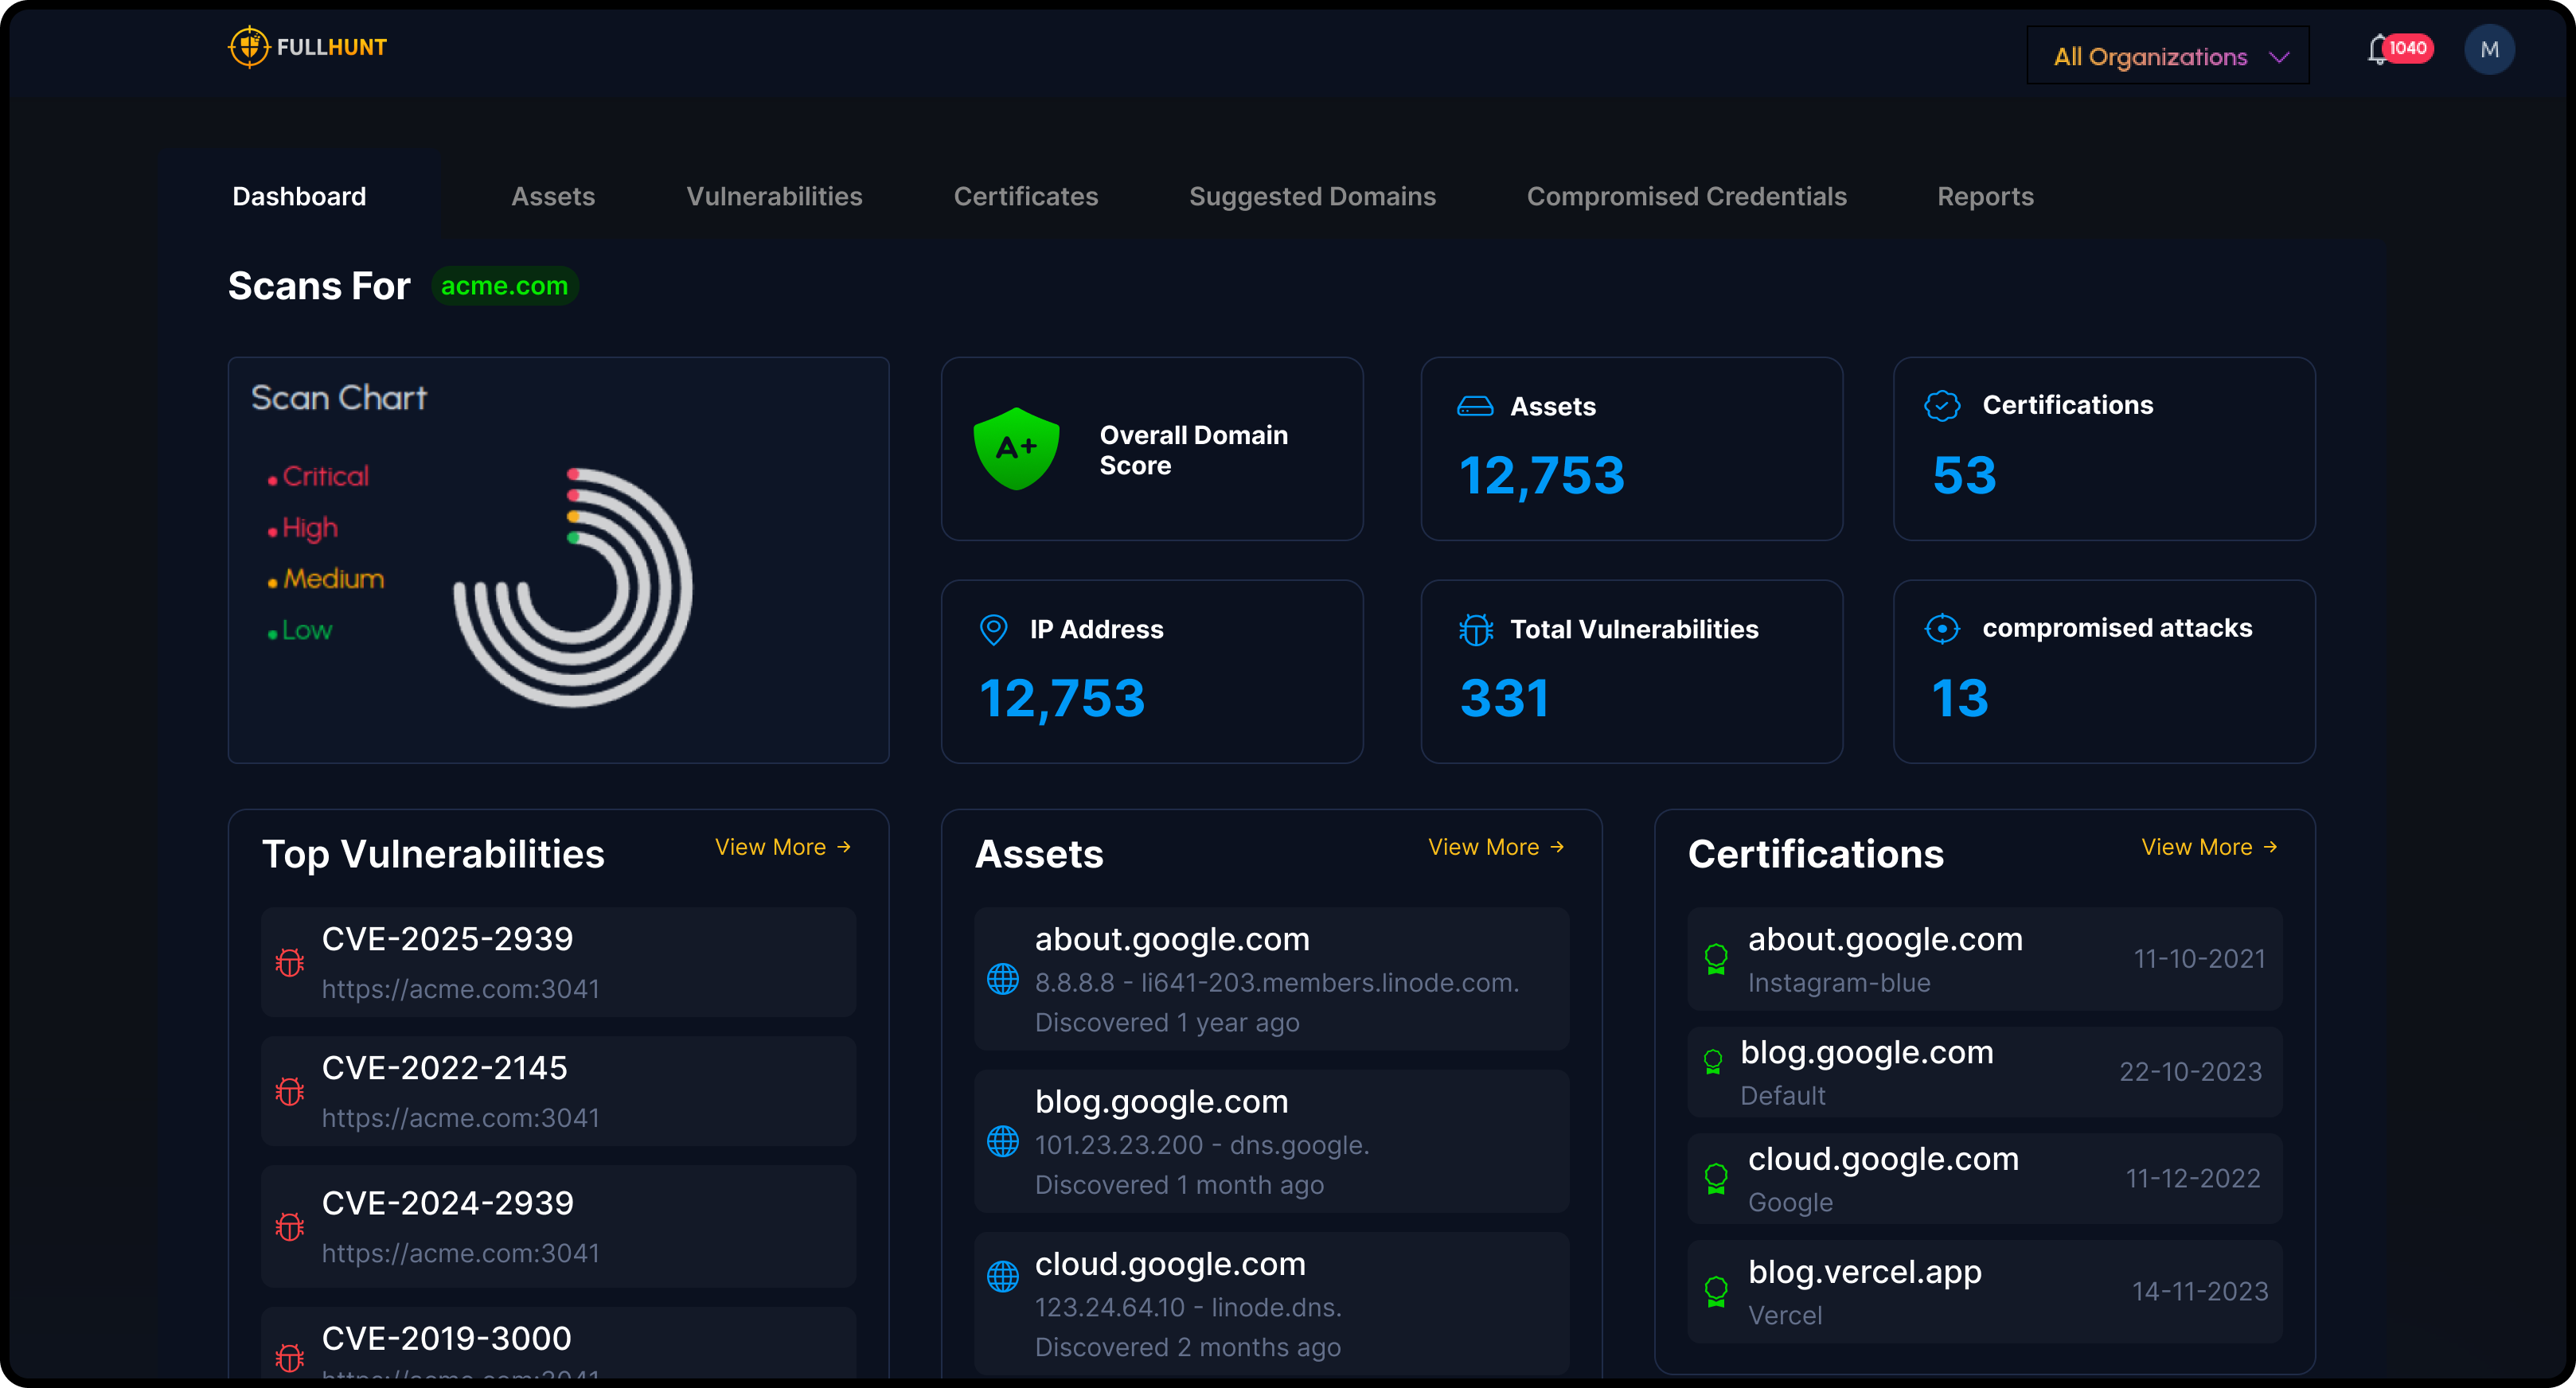
Each check is re-run against the live service before the finding is reported. Findings are enriched with exploit context, EPSS, and KEV data.
- Expired SSL certificates
- Misconfigurations
- Local file inclusion
- CVE-specific checks
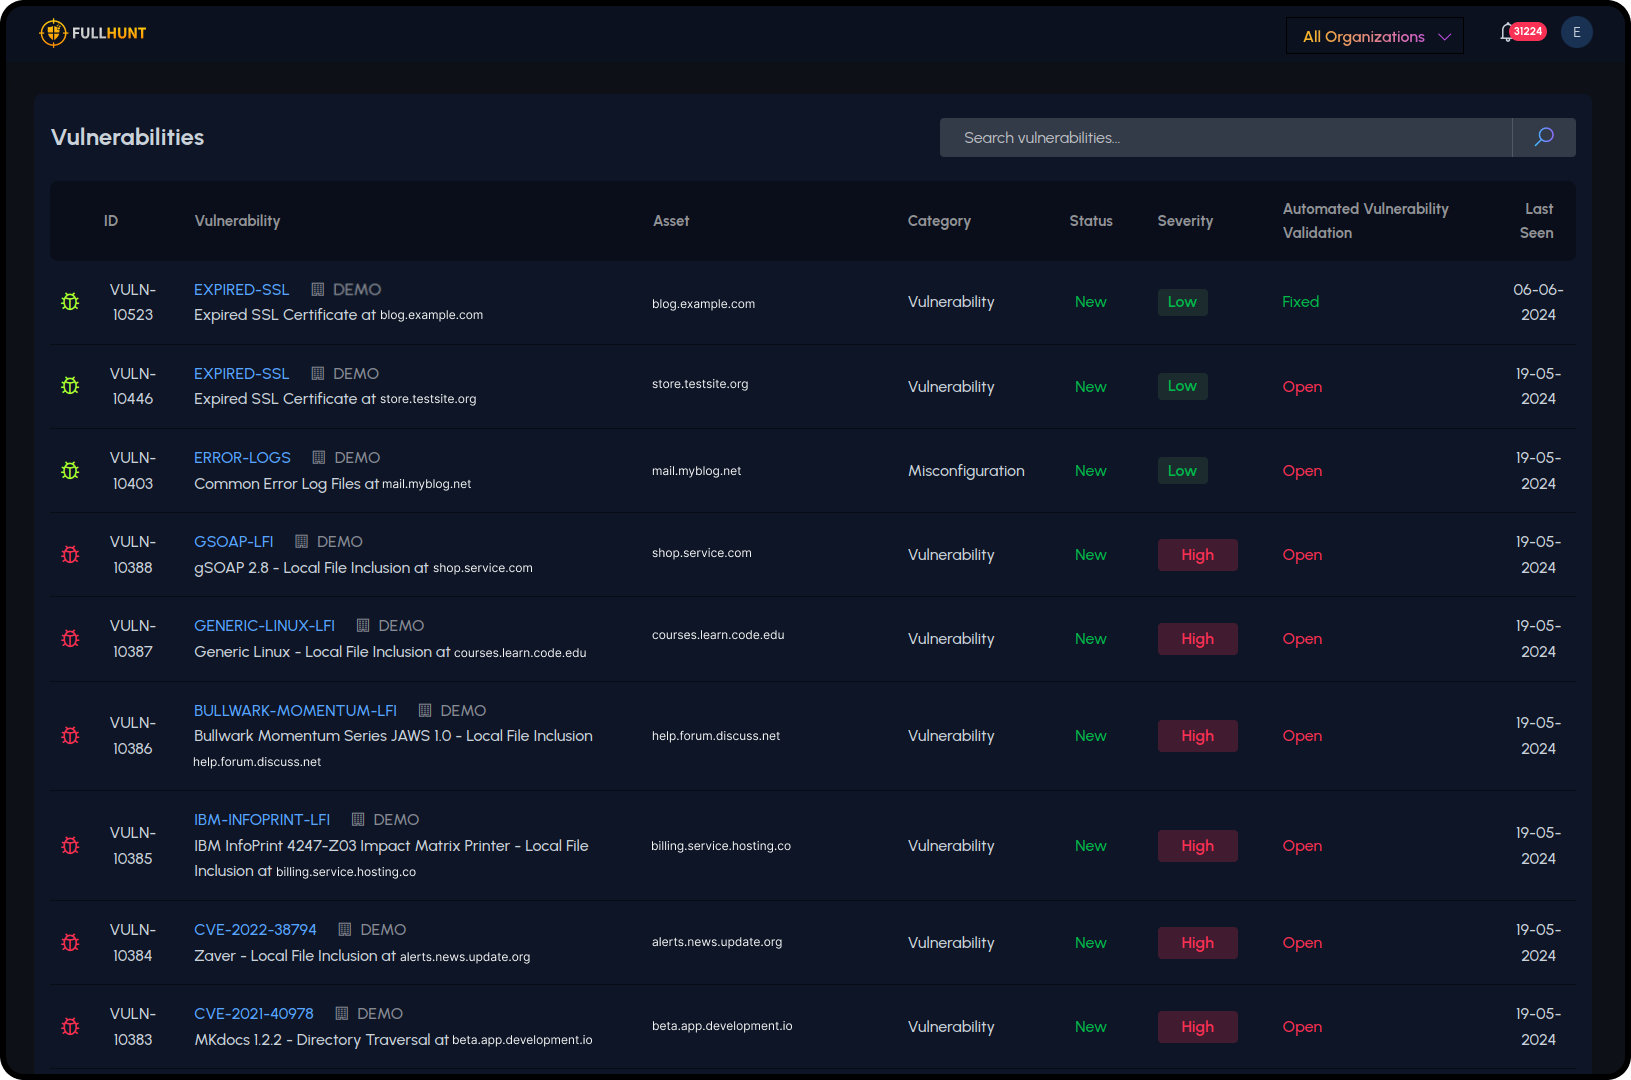
Every CVE enriched with exploit context.
EPSS scores, CISA KEV status, and 130,000+ tracked public exploits are layered onto your attack surface at the point the CVE is matched to a host.
Smaller Patch Queues
Every finding carries its CISA KEV status and its EPSS score. Work the KEV matches first.
Faster MTTR
The ticket opens with the EPSS score, the KEV status, and links to any tracked public exploit already on it.
Visibility beyond your own perimeter.
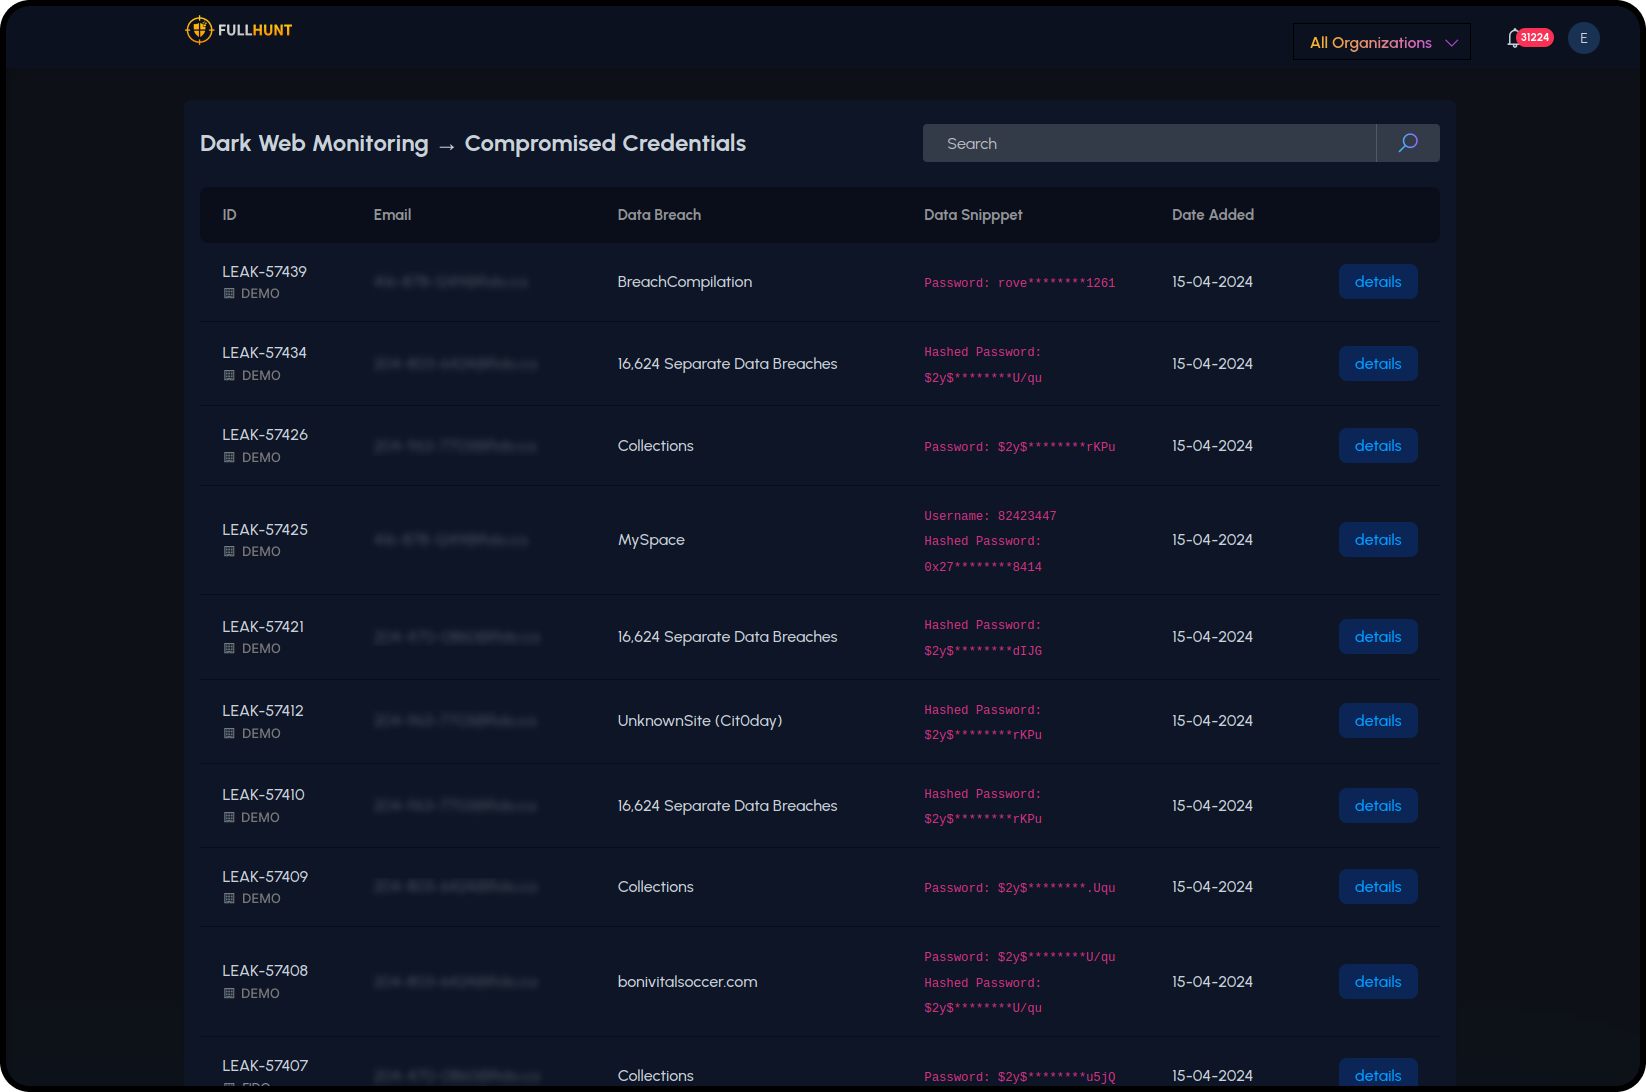
Credential leaks, breached accounts, and dark web mentions tied to your domains. Vendor and subsidiary exposure monitored continuously.
- Compromised credential alerts
- Typosquatting & phishing lookalikes
- Third-party vendor exposure scoring
- Subsidiary attack surface monitoring
Discover → Monitor → Validate → Integrate
Each cycle refreshes the asset inventory, validates exposed services, and routes findings to your existing tools.
01
Discover
Map your complete external footprint: domains, IPs, cloud, technologies, at internet scale.
02
Monitor
Track changes, new services, and configuration drift 24/7, with alerts routed where you work.
03
Validate
Runtime checks confirm real exploitability. EPSS and KEV enrich every finding.
04
Integrate
Push findings to Splunk, XSOAR, Jira, Slack, and more.
Why teams choose FullHunt Enterprise
Continuous Collection
Discovery and monitoring run 24/7, so an asset provisioned after a scan is picked up on the next pass.
High Signal, Low Noise
Runtime validation cuts false positives. Your team works on real issues.
Fits Your Workflow
Findings arrive in the SIEM, ticket queue, or channel your team already works from.
Fast Time to Value
Operational in under 30 minutes. See your entire external footprint in seconds.
Enterprise-ready from day one
SSO & RBAC
Enterprise auth and role-based access built in
External collection
FullHunt starts collecting from the public internet after you define the assets to monitor.
Agentless collection
FullHunt scans from the public internet, so you do not install agents or change network configuration.
Scales to 400K
Startups to Fortune 500
Ready to secure your attack surface?
Talk to our team or start a free trial.