Internet Intelligence for Enterprise Exposure Management
A dedicated platform for continuous asset discovery, exposure monitoring, vulnerability validation, dark web monitoring, and reporting.
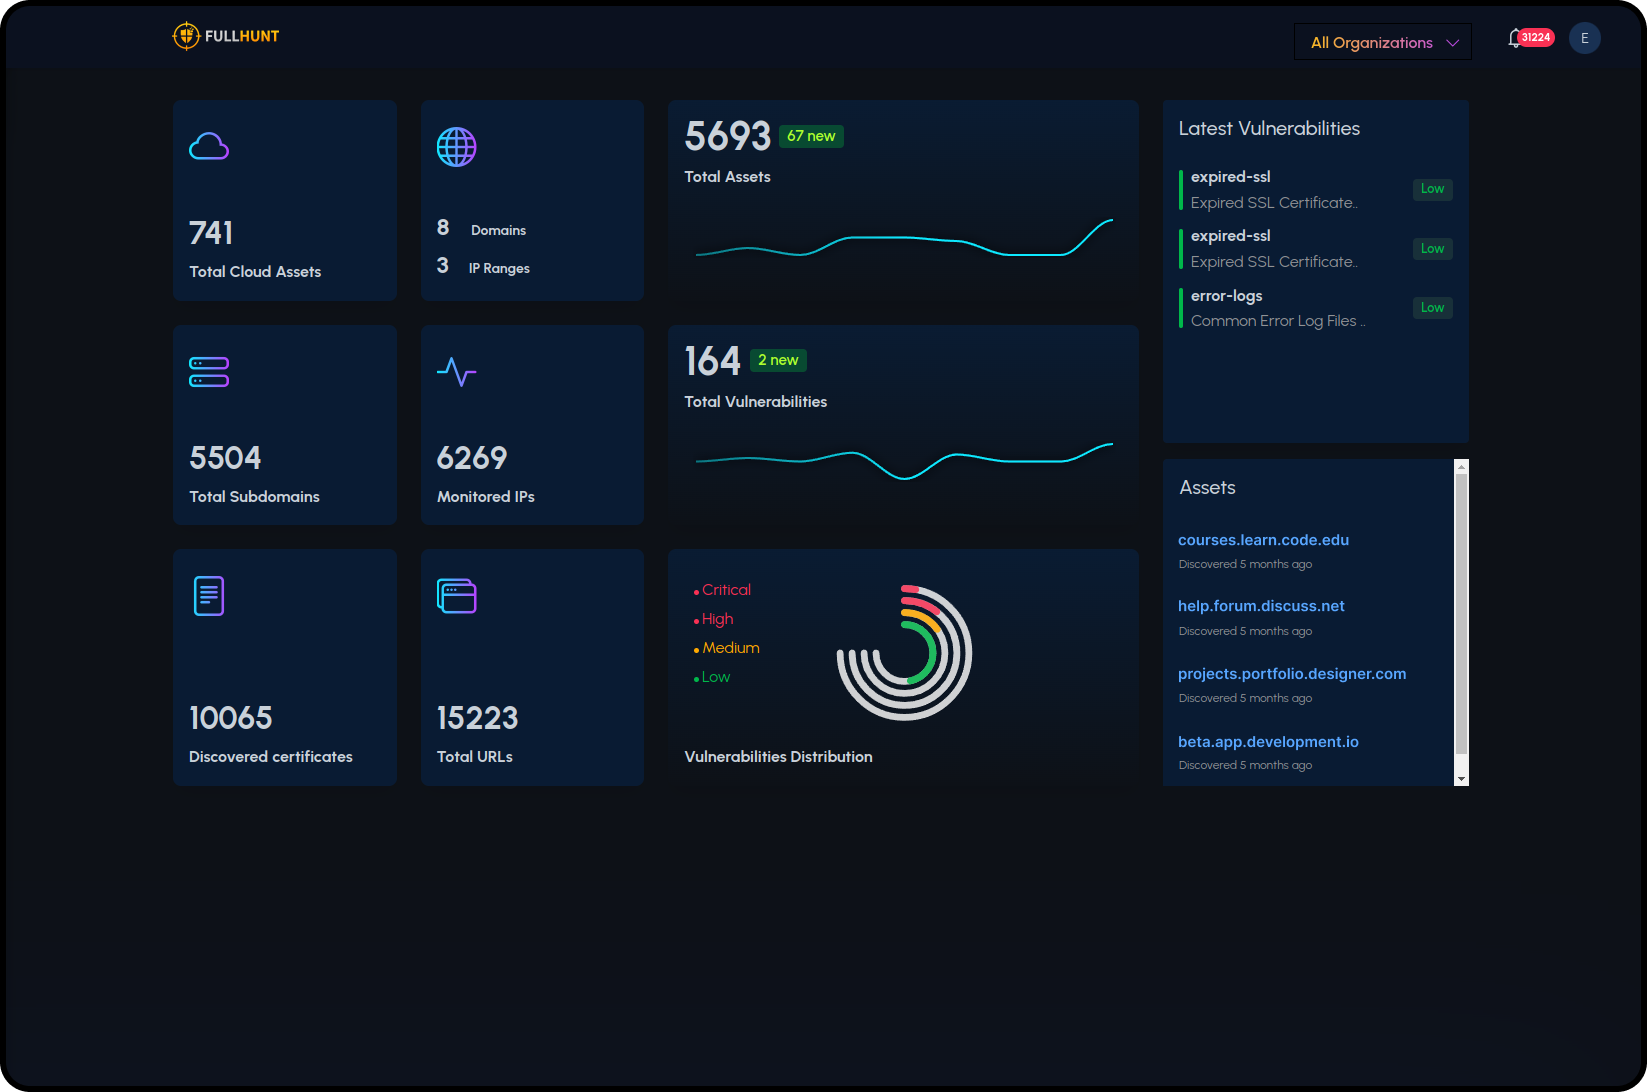
Discovery that runs on its own cycle
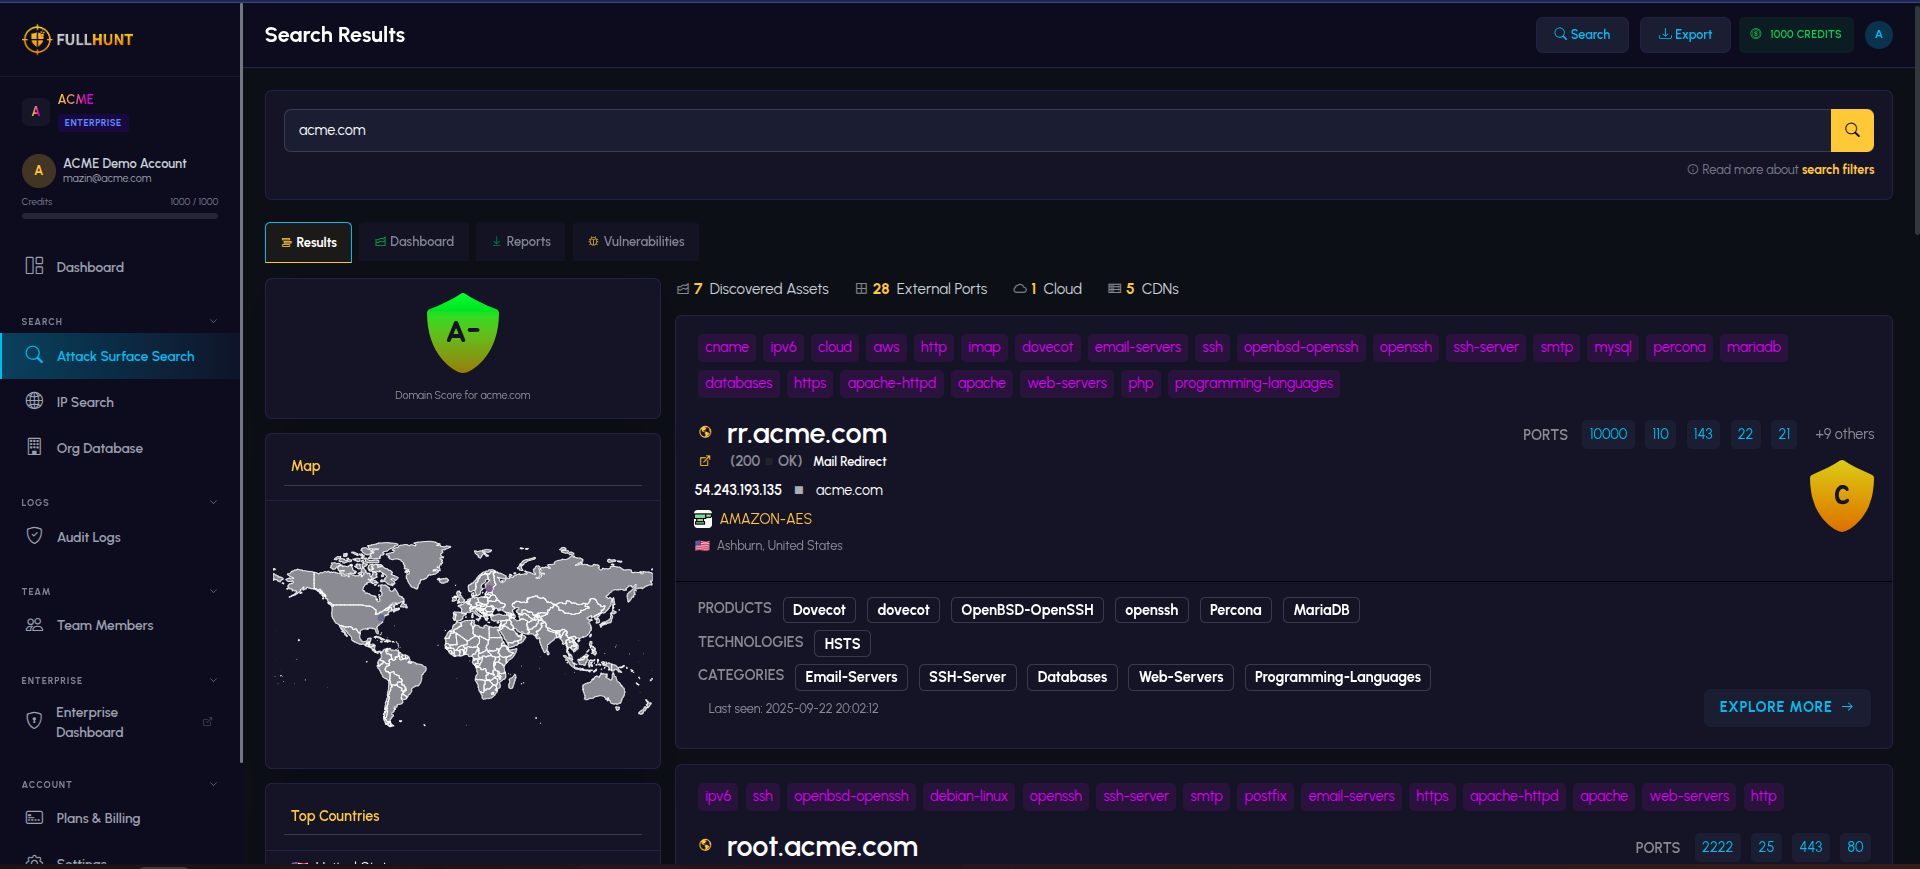
Point-in-time scans miss the assets that appear between assessments. FullHunt runs continuously, discovering new assets as they're provisioned, detecting configuration changes as they happen, and validating exposures against your live surface. A host provisioned today is picked up on the next collection pass, without waiting for a window you set.
Core Capabilities

Asset Discovery
Internet-scale enumeration: subdomains, IPs, cloud assets, and shadow IT discovered automatically without agents or network access.

Continuous Monitoring
Change detection and configuration drift tracking on a rolling collection cycle. New services, open ports and certificate changes surface on the pass that observes them.

Exposure Detection
Open ports, misconfigurations, expired certificates, and exposed admin panels surfaced automatically across your entire footprint.

Vulnerability Scanning
Runtime-validated checks map CVEs to exposed assets and keep the validation evidence with each finding.

Vulnerability and Exploit Intelligence
EPSS scoring, KEV alignment, and curated PoC tracking. Fix what attackers are actively exploiting first.

Dark Web Monitoring
Credential leaks and breached accounts tied back to your monitored domains. Know before attackers act.
Discover Assets From A Single Domain
Your attack surface grows every time a developer provisions a cloud resource, registers a domain, or spins up a service. FullHunt tracks it all without requiring agents, network access, or manual input.
- Automated subdomain enumeration at internet scale
- Cloud discovery across AWS, Azure, GCP, and more
- Technology fingerprinting with 7,000+ web and product signatures
- Organization and business unit attribution
- Certificate tracking and expiry monitoring
- Shadow IT and forgotten asset identification

Validate & Prioritize Vulnerabilities
Not all CVEs are equal. FullHunt runtime-validates every finding against your live assets and enriches them with real-world exploit intelligence so you fix the right things first.
- Runtime re-testing of each finding against the live service
- EPSS probability scoring for exploit likelihood
- CISA KEV tracking for actively exploited CVEs
- Public exploit and PoC correlation
- Per-asset risk scoring based on exploitability
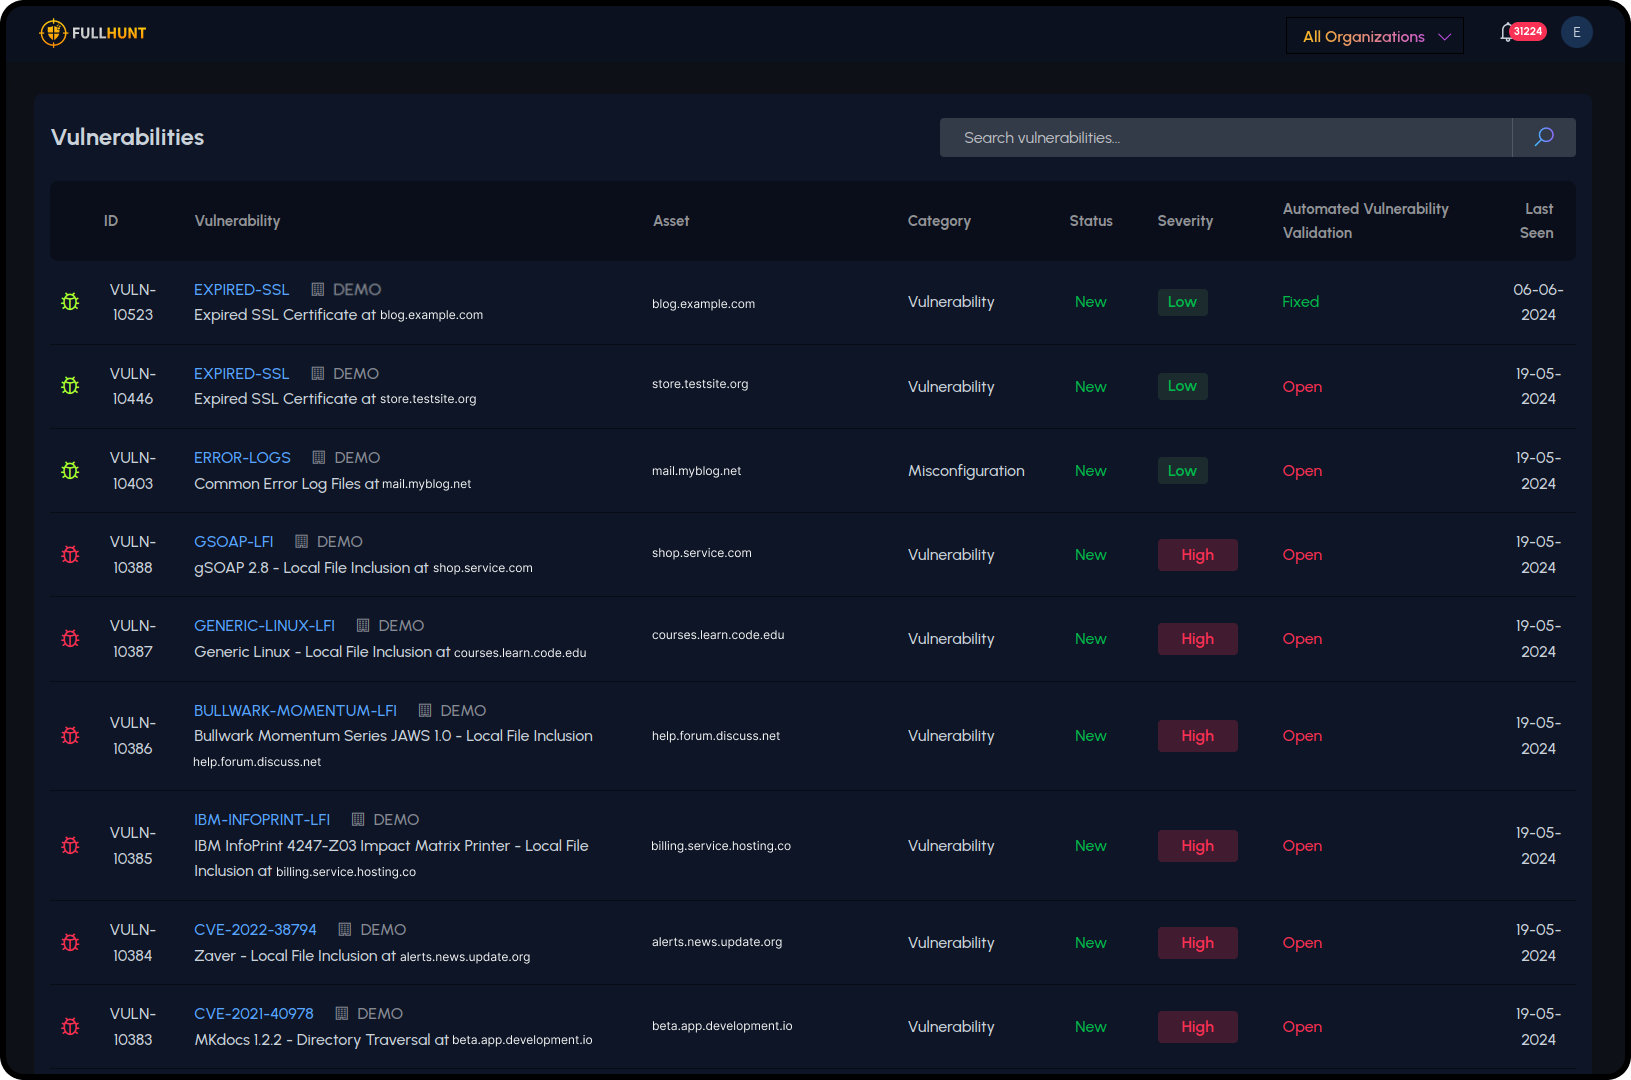
Monitor Changes Continuously
The threat landscape doesn't wait for your next scheduled scan. FullHunt watches your attack surface continuously and alerts on meaningful changes as they are observed.
- Configuration drift detection across all assets
- New service and port discovery alerts
- Certificate and DNS change tracking
- Rolling collection cycle rather than a fixed scan window
- Noise-filtered alerts on changes that matter
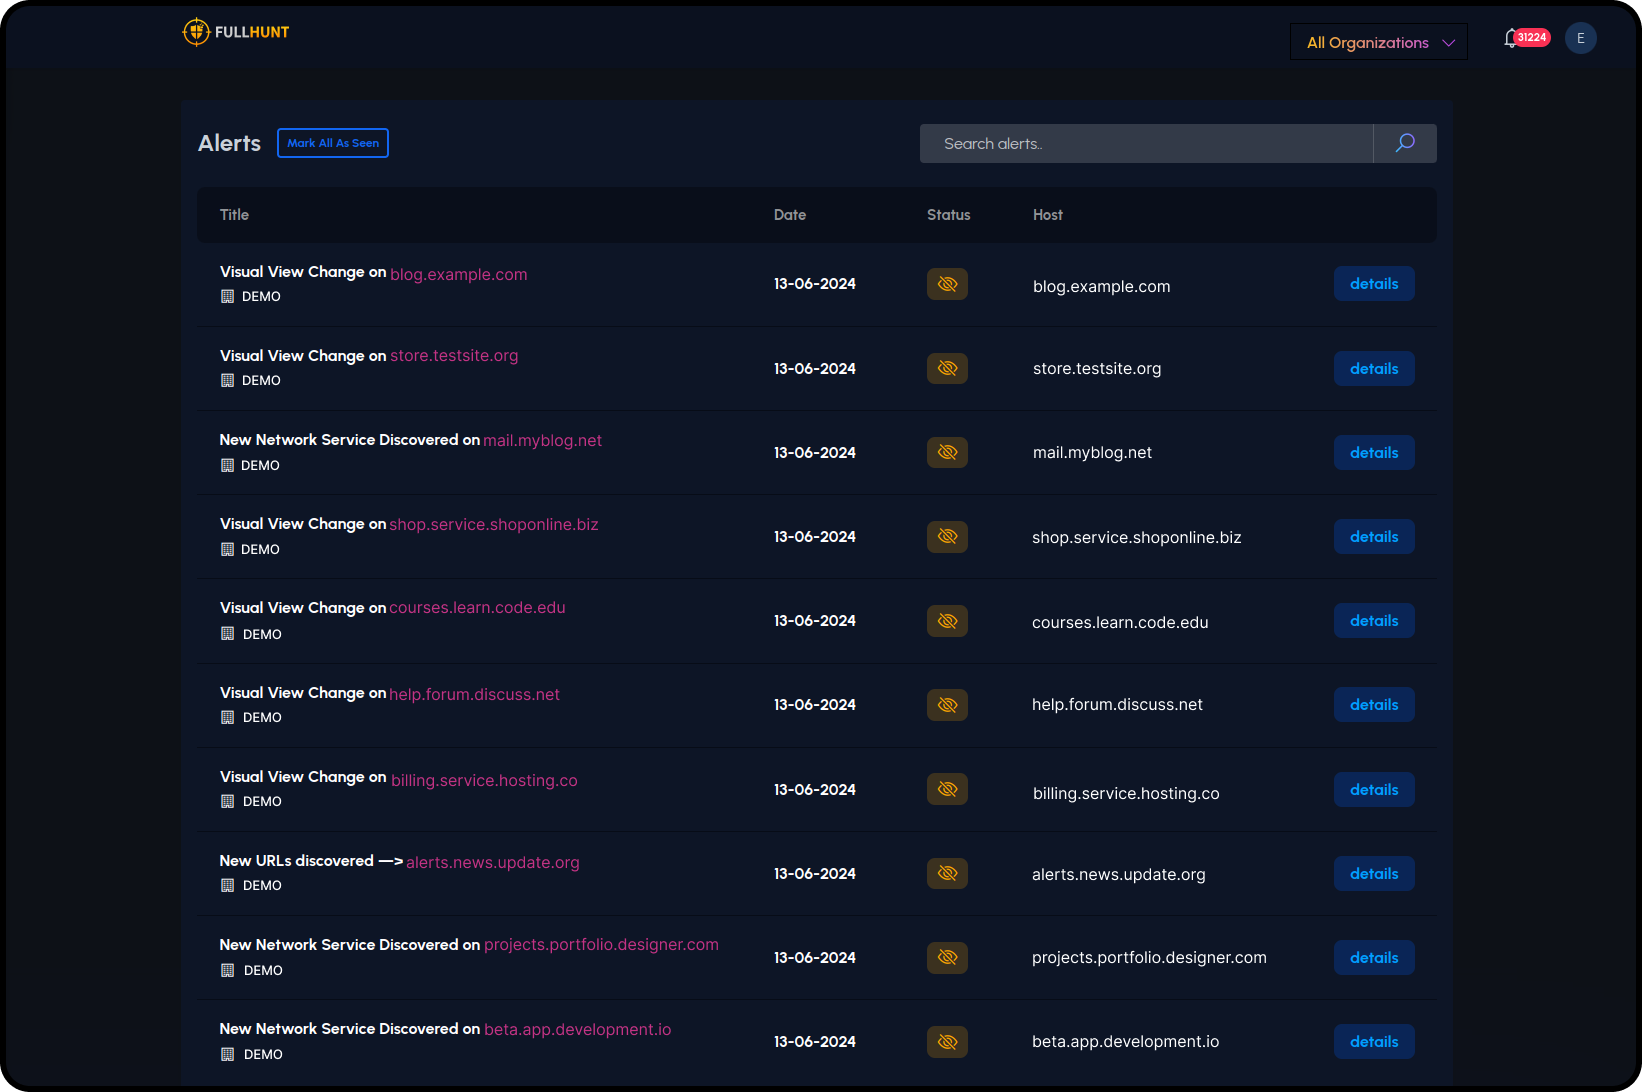
Route Issues Into Your Workflow
Findings are only useful if they reach the right people. FullHunt connects to your existing stack so vulnerabilities flow directly into the tools your team already uses.
- SIEM/SOAR: Splunk, XSOAR, FortiSOAR
- Ticketing: Jira, ServiceNow
- Chat & collaboration: Slack, Microsoft Teams
- Custom webhooks and REST API
- Exportable reports (CSV, JSON, PDF)
Key Outcomes
Shrink the Attack Surface
Decommission forgotten assets and close exposures faster with complete, always-current visibility into your external footprint.
Prioritize What Matters
Exploit context and asset criticality combined. Focus your team on findings with exploit evidence behind them.
Accelerate Remediation
Issues open as tickets in Jira or ServiceNow with the asset, the evidence, and the validation status already attached.

Built for MSSPs and Multi-Tenant Operations
Run a managed ASM practice or monitor multiple clients from a single pane of glass. FullHunt Enterprise supports fully isolated tenants, unified dashboards, automated reporting, white-label branding, and role-based access control.
- Isolated per-client environments with unified visibility
- Automated scheduled reports across all tenants
- White-label ready. Present under your own brand.
- RBAC for team-level and client-level access control
Beyond Your Perimeter
FullHunt Enterprise extends to any scope you care about: subsidiaries, acquired companies, third-party vendors, or one-time assessments. Provide a domain or IP range and get results in minutes, agentlessly.
Subsidiary Monitoring
Discover and monitor security across all subsidiary companies and business units.
Vendor Assessments
Assess a vendor without sending a questionnaire or asking for access to their environment.
M&A Due Diligence
Rapidly assess an acquisition target's external posture before a deal closes.
MSSP Client Coverage
Standardize assessments across clients with consistent methodology and automated reporting.
Findings go where your team already works
Native Integrations


Why Teams Choose FullHunt Enterprise
Continuous Collection
Unlike periodic scans, FullHunt runs continuously. Catch changes as they happen with no blind spots between assessments.
High Signal, Low Noise
Each finding is re-tested against the live service before it is reported, and the response that confirmed it is stored alongside it.
Built to Integrate
FullHunt sends findings to supported SIEM, ticketing, and chat tools, so your team can act without manual exports.
Fast Time to Value
Get operational in under 30 minutes, then see your external footprint in seconds.
Ready to secure your attack surface?
See how FullHunt Enterprise can support your exposure-management program.